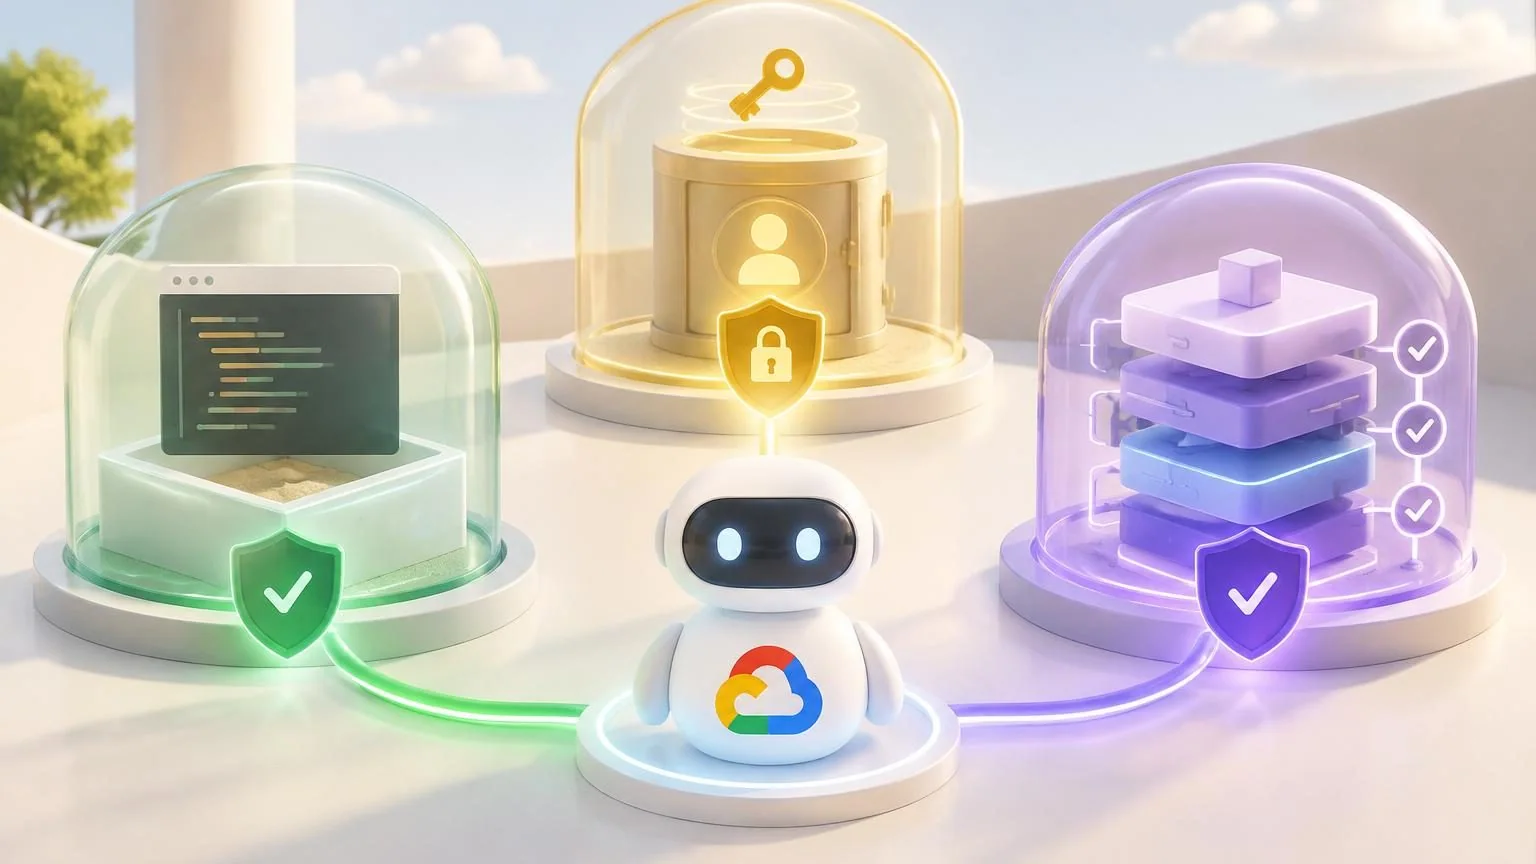
Google Cloud’s November 4–6, 2026 updates address three parts of agent security: the environment in which code is tested, credentials used to reach services, and reusable skills installed into agents. The announcements mix generally available capabilities with previews, so maturity labels matter.
Code verification gets explicit isolation choices
At its November 4 Security Summit, Google described new CodeMender capabilities for running vulnerability verification and exploit simulation in either an operating-system sandbox or an isolated virtual machine. The preview also adds human checks for local writes and command execution, plus scanning at folder, repository, or changed-file scope.
This is an expansion of an existing preview, not the first release of CodeMender. The controls are relevant because reproducing a security weakness can involve executing deliberately hostile behavior. A generated patch and a successfully contained verification environment answer different security questions.
Delegated access has a separate control plane
The same announcement identifies Auth Manager as generally available. Google’s documentation describes centralized management of user-delegated credentials, with IAM access controls and OAuth handling. The announcement separately labels Agent Identity JWT support as a preview. Those statuses should not be collapsed into a claim that every identity mechanism is generally available.
A managed credential system can reduce the need for application code to store and refresh tokens itself. It does not remove the need to choose the right service, user scope, and authorization boundary for each action.
Reusable skills become governed resources
November 6 release notes mark standalone Agent Registry skills generally available. The resource model includes skills, immutable revisions, and publisher details. The notes also announce security scanning of standalone skill revisions, reviewable findings, organization policy controls, and least-privilege management access. Customer-managed encryption for skill payloads is separately marked preview.
The scanning documentation provides the operational path for inspecting findings. A registered revision and a completed scan are useful evidence, but neither should be presented as a guarantee that a package is appropriate for every agent or business task.
Connect the safeguards to an actual assignment
Our engineering analysis is to evaluate a complete small workflow. Identify the exact skill revision, the files and services it can reach, the identity authorizing access, and the environment executing commands. Verify what happens when a permission is absent or revoked halfway through a task.
For security testing, start with an authorized isolated target and check where generated artifacts and logs land. A virtual machine can contain execution while an overly broad credential still exposes an external service. Isolation and least privilege therefore need independent checks.
For a shared skill catalog, decide who can publish, approve, and withdraw a revision. Record the revision used by a completed task so a later finding can be traced to affected executions. Review findings in context rather than letting a package’s presence in a registry become automatic approval.
The significance of the week’s updates is their coverage of different boundaries. Reliable adoption depends on composing those controls deliberately, retaining a clear record of who authorized an action and which software performed it.